
Artificial intelligence (AI) is transforming the way businesses operate. Companies increasingly rely on AI-powered tools to analyse information, automate administrative tasks, generate marketing content, support customer service, review documents, and improve decision-making. While these technologies offer significant opportunities, they also introduce legal and regulatory challenges that businesses cannot afford to ignore.
For organisations operating in Thailand, adopting AI is not simply a technology decision. It can involve personal data protection, confidentiality, intellectual property, contractual obligations, cybersecurity, and accountability for automated processes. Companies using international platforms may also need to consider legal requirements in other jurisdictions.
Effective AI governance helps businesses identify these risks before they become disputes, regulatory problems, or reputational crises. Rather than preventing innovation, a clear legal framework enables organisations to adopt AI more confidently and responsibly.
This article examines seven important legal considerations that businesses should address when implementing AI systems in Thailand.
Personal Data Protection and Thailand’s PDPA
One of the first questions businesses should ask is whether their AI systems collect, process, analyse, or generate information relating to identifiable individuals. Such activities may fall within the scope of Thailand’s Personal Data Protection Act B.E. 2562 (PDPA).
AI applications may process personal information from customer databases, employee records, email communications, online forms, recorded conversations, photographs, and other sources. Even when a business does not develop its own AI model, using a third-party AI service to process personal data can raise important compliance questions.
Businesses should assess the legal basis for processing, the purposes of collection, transparency obligations, data minimisation, retention periods, and the rights of data subjects. Where sensitive personal data is involved, additional legal requirements may apply.
Organisations should also understand whether information submitted to an external AI provider may be retained, reviewed, used to improve a service, or transferred to another jurisdiction. These details should be evaluated before employees upload personal information into AI tools.
Practical steps for businesses
- Identify the personal data used by each AI application.
- Document the purpose and legal basis for relevant processing activities.
- Review privacy notices and internal data protection policies.
- Assess whether an AI provider acts as a data processor or has another legal role.
- Review retention, security, and international data transfer arrangements.
- Restrict the use of sensitive or confidential information in unapproved AI tools.
AI adoption should be integrated into the organisation’s broader PDPA compliance programme rather than treated as a separate technical project.
Confidential Information and Trade Secrets
Employees may use AI assistants to summarise contracts, analyse financial information, prepare presentations, or draft business proposals. However, entering confidential information into an external service can create risks that are not immediately obvious.
Depending on the provider’s terms and technical configuration, submitted information may be stored, processed by subcontractors, or retained for defined periods. Access controls and confidentiality protections can differ substantially between consumer applications and enterprise services.
Information exposed through inappropriate AI use may include customer lists, pricing strategies, source code, transaction documents, business plans, product designs, and trade secrets. Once information is disclosed outside an organisation’s intended control, recovering that control may be difficult.
Businesses should establish clear rules defining which AI tools employees may use and which categories of information may be submitted. Confidentiality agreements, employee policies, vendor contracts, and technical safeguards should support one another.
Practical steps for businesses
- Create an approved list of AI applications.
- Classify information according to its sensitivity.
- Prohibit uploading restricted information without prior authorisation.
- Review vendor data handling and confidentiality terms.
- Train employees to recognise AI-related disclosure risks.
Clear internal rules can reduce accidental disclosure while allowing employees to benefit from approved AI technologies.
Intellectual Property and Ownership of AI-Generated Content
AI tools can produce marketing copy, illustrations, software code, product descriptions, reports, and other creative material. Businesses may assume that purchasing access to an AI service automatically gives them unrestricted ownership of everything it generates. That assumption can create legal uncertainty.
Intellectual property questions may arise concerning the ownership and protectability of AI-generated output, the rights granted by the provider’s terms, the use of third-party material in generated content, and the incorporation of protected works into commercial products.
Under Thai intellectual property law, the protection available for a particular output depends on the applicable legal requirements and the circumstances in which it was created. The involvement of AI does not eliminate the need to assess authorship, originality, ownership, and third-party rights.
Businesses should also consider whether AI-generated material resembles existing trademarks, reproduces protected creative works, or includes code subject to third-party licence obligations. Publishing content commercially without appropriate review can expose an organisation to complaints and disputes.
Practical steps for businesses
- Review the intellectual property terms of AI providers.
- Check generated content before commercial publication.
- Maintain records of human contributions, editing, and approvals.
- Review third-party licences when AI-generated code is used in software.
- Use appropriate contractual provisions to clarify ownership and permitted use.
AI can support creative work, but it should not replace an organisation’s intellectual property review process.
Liability for AI-Assisted Decisions and Incorrect Outputs
AI systems can generate inaccurate information, fabricated references, misleading recommendations, or incomplete analyses. These errors may be particularly problematic when businesses use AI to support customer communications, recruitment, financial analysis, legal documentation, or other consequential decisions.
For example, an organisation could rely on an incorrect AI-generated statement in a commercial proposal or publish an inaccurate description of a competitor. An automated system could also produce an unfair recommendation because of limitations in its training data or design.
The allocation of legal responsibility depends on the relevant facts, the applicable law, contractual arrangements, and the conduct of the parties involved. Using AI does not automatically transfer a business’s legal responsibilities to the technology provider.
Organisations should therefore identify which AI outputs require human verification and which decisions must remain subject to appropriate human oversight. The level of review should reflect the potential consequences of an error.
Practical steps for businesses
- Require human review for high-impact or legally significant outputs.
- Verify factual claims, references, calculations, and citations.
- Maintain records of important AI-assisted decisions.
- Establish escalation procedures for errors and complaints.
- Define clear responsibility for approving AI-generated material.
Human accountability is an important component of responsible AI governance, particularly where decisions can affect customers, employees, or business partners.
Cybersecurity and AI Vendor Risk
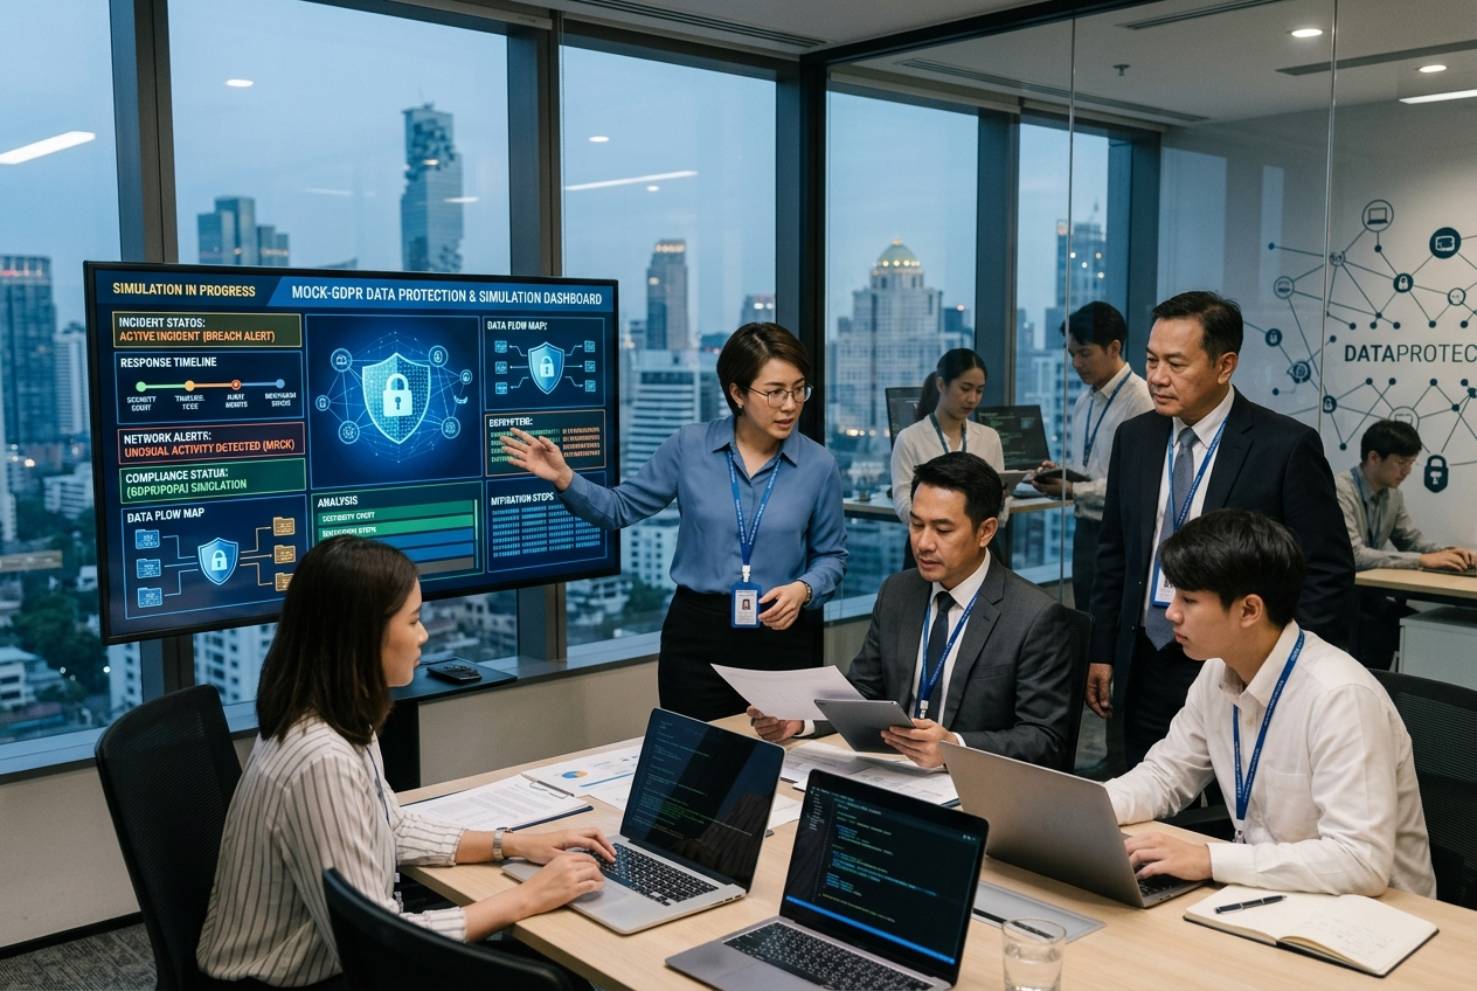
AI systems can introduce additional security risks into an organisation’s technology environment. These may include unauthorised access to sensitive information, insecure integrations, excessive user permissions, malicious instructions embedded in external content, and weaknesses in connected applications.
Third-party AI services may also involve complex arrangements among service providers, cloud hosting companies, software developers, and other subcontractors. Businesses should understand which parties can access their information and what safeguards apply.
Where a cybersecurity incident involves personal data, the organisation may need to assess its obligations under the PDPA and other applicable laws. Depending on the circumstances, breach notification, investigation, remediation, or other regulatory requirements may arise.
Practical steps for businesses
- Conduct security assessments before deploying AI applications.
- Review access controls, encryption, logging, and incident response procedures.
- Evaluate the security practices of AI providers and subcontractors.
- Limit AI system access to the information and functions required for its purpose.
- Include AI-related scenarios in cybersecurity incident planning.
Vendor due diligence should address not only the functionality and price of an AI service but also its security, privacy, and contractual implications.
Contracts, Service Terms, and Cross-Border Processing
Businesses often adopt AI platforms through standard online terms and subscription agreements. These documents may determine how submitted information is processed, who is responsible for security, what happens when the service is unavailable, and which remedies are available if a dispute arises.
Organisations should pay particular attention to data processing provisions, confidentiality obligations, intellectual property terms, service limitations, liability clauses, termination rights, and data deletion arrangements.
Cross-border processing deserves additional scrutiny. If personal data originating in Thailand is transferred to another country, the organisation must assess the applicable PDPA requirements and relevant exceptions, safeguards, or transfer mechanisms. The analysis depends on the circumstances and the parties involved.
Businesses should not assume that a provider’s general statement of compliance is sufficient to resolve every legal obligation. The contract and the actual data flows must be examined together.
Practical steps for businesses
- Review the provider’s terms before accepting them.
- Identify where information is stored and processed.
- Assess international data transfer requirements where applicable.
- Clarify security responsibilities and incident notification procedures.
- Check termination, data export, and deletion provisions.
- Ensure vendor arrangements align with internal policies and customer commitments.
Contractual review can help businesses understand their obligations before they become dependent on an AI provider.
Internal AI Policies, Employee Training, and Accountability
Even a carefully selected AI tool can create problems if employees do not understand how it should be used. Informal adoption can lead to inconsistent practices, unauthorised data disclosure, unreliable outputs, and unclear responsibility for business decisions.
An internal AI policy should explain the organisation’s permitted uses of AI, prohibited activities, data handling requirements, approval procedures, and expectations for human review. It should also establish how employees can report incidents or request approval for new applications.
Businesses may benefit from assigning responsibility for AI governance to a designated team or accountable manager. Depending on the organisation’s size and risk profile, this responsibility may involve legal, compliance, IT, cybersecurity, data protection, human resources, and business operations teams.
Policies should be reviewed as technology, business practices, and applicable legal requirements evolve. Employees should receive practical training that reflects the tools they actually use and the risks associated with their roles.
Practical steps for businesses
- Adopt a written AI acceptable-use policy.
- Maintain an inventory of AI applications and their business purposes.
- Define approval requirements for higher-risk uses.
- Assign responsibility for monitoring compliance and reviewing incidents.
- Train employees on privacy, confidentiality, security, and accuracy.
- Review policies regularly and when significant systems change.
Good governance turns AI use from an informal collection of individual practices into a controlled business process.
How Businesses Can Build a Practical AI Governance Framework
Organisations do not necessarily need to begin with a complex governance programme. A structured assessment can help identify the most important risks and establish proportionate controls.
- Identify AI use cases: Document the tools in use, their purposes, and the departments relying on them.
- Classify the risks: Assess whether each use case involves personal data, confidential information, important business decisions, or external publication.
- Review legal obligations: Evaluate applicable privacy, intellectual property, cybersecurity, contractual, and sector-specific requirements.
- Assess providers: Examine vendor terms, data handling practices, security controls, and subcontracting arrangements.
- Implement safeguards: Establish access restrictions, human review, documentation, and incident response procedures.
- Train employees: Communicate approved practices and explain how to report potential problems.
- Monitor and improve: Reassess the framework as new AI applications, business requirements, and legal developments emerge.
The objective is to match governance measures to the risks presented by each application rather than apply the same controls to every AI use case.
Why Legal Advice Matters for AI Adoption in Thailand
AI governance sits at the intersection of technology, business operations, and law. A technical solution may reduce one type of risk while leaving contractual, privacy, or intellectual property questions unresolved.
Legal review can help businesses determine which obligations apply, evaluate their contractual exposure, clarify responsibility between providers and customers, and establish appropriate internal policies. It can also help organisations identify where existing privacy notices, employee agreements, vendor contracts, or website documentation may require updates.
For companies operating internationally, the assessment may need to consider more than one legal system. The relevant obligations will depend on factors such as the organisation’s activities, the people whose data is processed, the location of processing, and the services involved.
Because AI regulation and related guidance continue to develop, businesses should verify the current legal position before deploying systems that involve significant personal data, sensitive information, or consequential automated decisions.
Conclusion: Responsible AI Starts with Legal Preparedness
Artificial intelligence can help businesses improve efficiency, develop new services, and make better use of information. However, its commercial benefits should be supported by appropriate legal and operational safeguards.
For businesses in Thailand, the essential priorities include PDPA compliance, confidentiality, intellectual property protection, accountability, cybersecurity, vendor contracts, and employee governance. Addressing these issues early can reduce avoidable risks and support more sustainable technology adoption.
AI governance should not be treated as a one-time checklist. It is an ongoing process that combines legal assessment, technical controls, employee awareness, and regular review.
Need guidance on digital law and AI-related legal risks? Pim Legal provides specialist legal support in data protection, online law, cybersecurity, website compliance, and related digital legal matters. Businesses can seek tailored advice to assess their obligations and develop an appropriate compliance framework.